Exploring what is inside the ASP.NET Core cookies
What is inside the .AspNetCore.Cookies authentication cookie, the session and antiforgery cookies, how Data Protection encrypts them, and how to look inside.
Read more →What is inside the .AspNetCore.Cookies authentication cookie, the session and antiforgery cookies, how Data Protection encrypts them, and how to look inside.
Read more →How to debug cookie problems in ASP.NET Core: cookies the browser rejects, cookies missing from requests, lost cookies and the SameSite rules behind them.
Read more →How the BearerToken authentication handler in ASP.NET Core 8 works, what its access and refresh tokens contain, and how it compares to Cookie and JwtBearer.
Read more →Debug missing claims in ASP.NET Core JwtBearer: inspect the access token, MapInboundClaims, the name and role claim types, and a claims diagnostic endpoint.
Read more →How to fix missing OpenID Connect claims in ASP.NET Core: check the ID token and UserInfo, claim actions, claim mapping, and the name and role claims.
Read more →How to troubleshoot JwtBearer authentication in ASP.NET Core APIs: 401 vs 403, middleware order, the WWW-Authenticate error details and the authentication logs.
Read more →The difference between IdentityResource, ApiResource and ApiScope in IdentityServer, and how identity scopes, access scopes and API resources shape tokens.
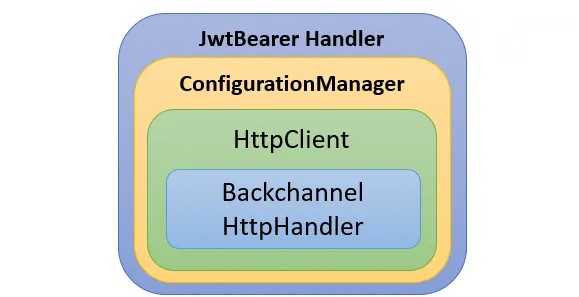
Read more →What changed in the ASP.NET Core JwtBearer library from 3.1 to 6: MapInboundClaims, a custom back-channel HttpClient, refresh intervals and token validation.
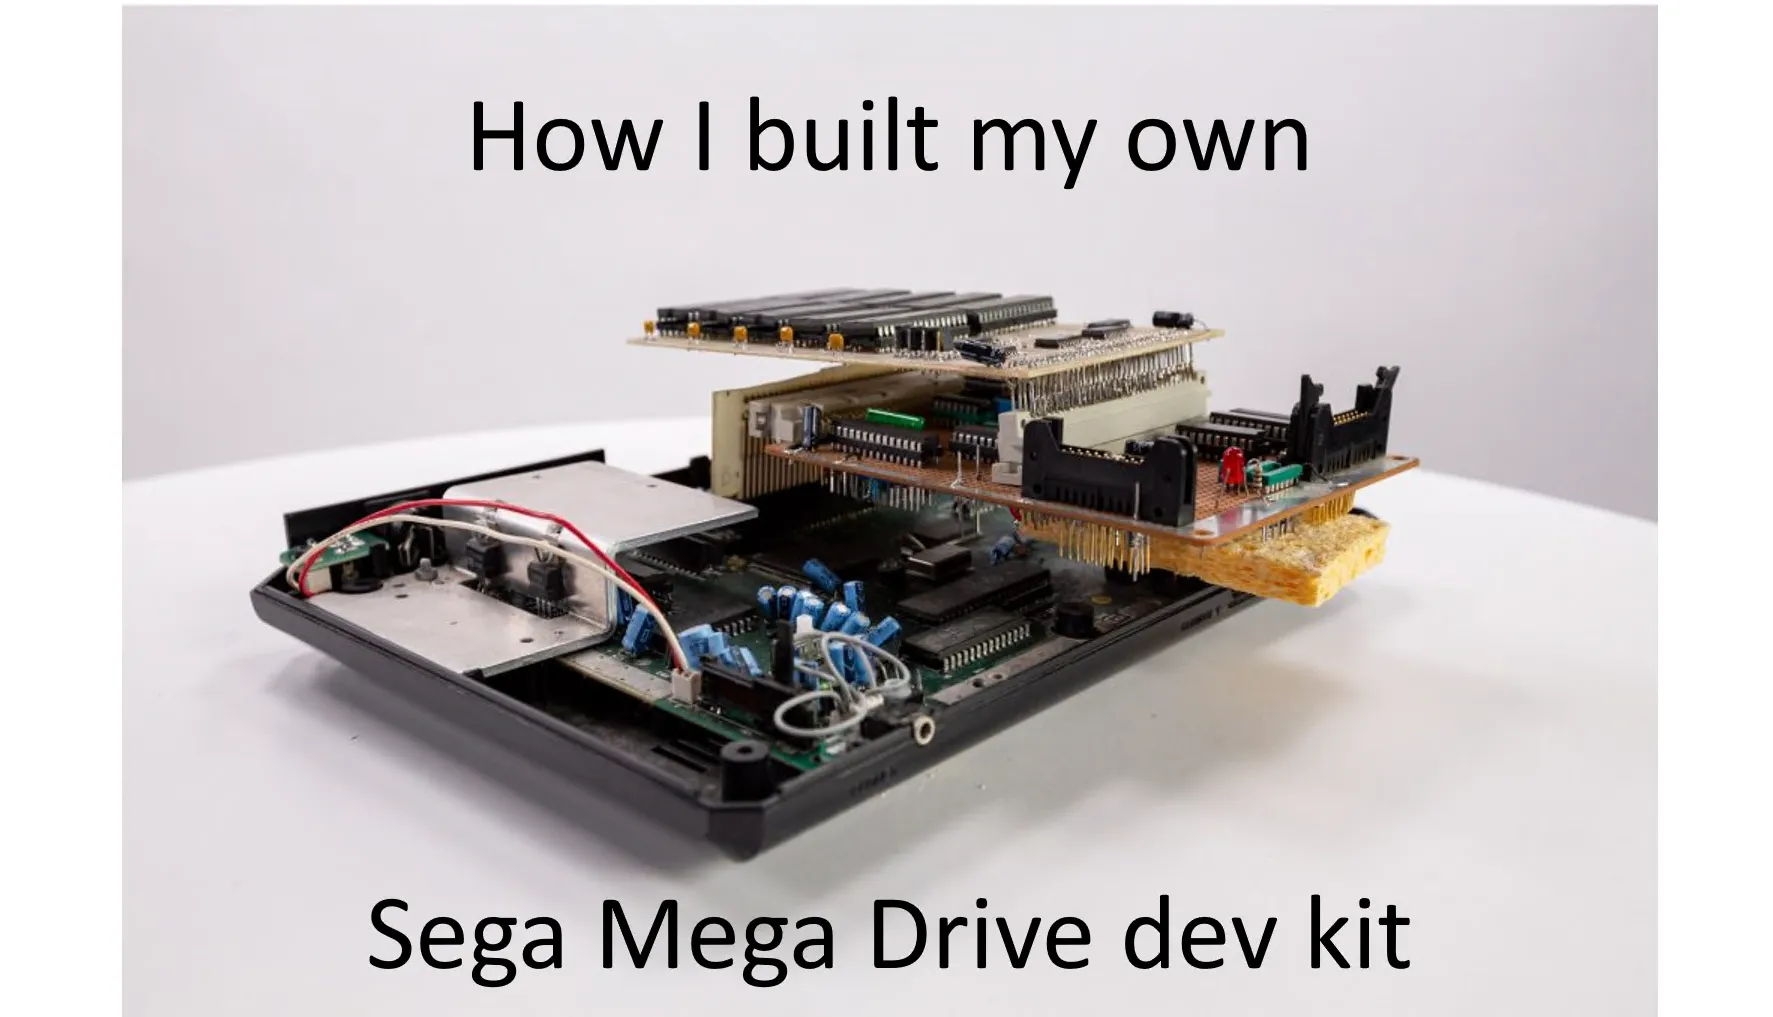
Read more →How I built a Sega Mega Drive dev kit from scratch: reverse engineering the cartridge slot, a homemade logic analyzer, a RAM cartridge and boot firmware.
Read more →TNValidate, a C# validation library with a fluent interface for defining validation rules, is now open source on GitHub. A short look at how to use it.
Read more →